



Introduction
Riverlight Gathering already has a working IPv4 event guide. Visitors need the same complete guide over IPv6, including its arrival information and downloadable programme. The network addresses are prepared, but the web service does not yet listen for IPv6 and the guide's AAAA record points to the wrong address.
You will separate those two problems: make direct IPv6 application access work first, then repair the name. You will preserve IPv4, the welcome desk, other DNS records and all original page/download bytes. Basic terminal, path and tab use and recognizing addresses, names and ports are prerequisites; Nginx and IPv6 administration are not. The 70-minute duration is an author estimate.
Guide Server and Guide Client are isolated network nodes sharing this training instance's kernel. They are not separate VMs. Change only guide.conf listener statements and the target AAAA/SOA serial in guide.zone; save downloads in the client workspace. Do not change routes, addresses, IPv6 switches, other sites, source pages or platform settings. This is a prepared local network, without public IPv6, RA, DHCPv6, tunnels or NAT64.
Compare the Address Families
In this step, you will read the working IPv4 guide, then distinguish a reachable IPv6 address from a listening application. Begin in Guide Client. This terminal starts in /home/labex/project/ipv6-guide/client; its shell and directory persist independently of Guide Server. pwd prints the current directory:
pwd
IPv4 addresses use four decimal parts, such as 10.77.0.10. IPv6 uses eight groups of hexadecimal digits. Leading zeroes in a group may be omitted; one :: replaces a run of all-zero groups. Here fd77:7::10 means fd77:0007:0000:0000:0000:0000:0000:0010. Its final 10 is hexadecimal, not the decimal final part of the IPv4 address. These private training addresses do not imply public Internet reachability.
curl retrieves an HTTP resource. -4 forces IPv4, -f treats HTTP error responses as failure, -s hides progress and -S still shows errors. --noproxy '*' bypasses proxies for every host; quotes keep * literal rather than expanding filenames. Port 8080 selects the guide application. -o saves received bytes to a file; v4 is a prepared output directory:
curl --noproxy '*' -4 -fsS http://guide.riverlight.test:8080/index.html -o v4/index.html
A successful save normally prints nothing. head -c 180 reads the first 180 bytes without changing the file:
head -c 180 v4/index.html
Expect HTML containing Riverlight Gathering. This is the working reference you will preserve. The page's full browser appearance needs its stylesheet, which you will save later.
Now test the prepared IPv6 address. ping -6 sends IPv6 echo requests; -c 1 stops after one. It tests network reachability rather than HTTP:
ping -6 -c 1 fd77:7::10
Expect a reply. For an IPv6 literal in a URL, square brackets separate the address's colons from the port separator. Quote the whole URL. -6 forces IPv6; --max-time 3 bounds the request to three seconds:
curl --noproxy '*' -6 -fsS --max-time 3 'http://[fd77:7::10]:8080/'
This request is expected to fail with curl: (7) and a refused connection. The IPv6 address exists and replies to echo, but the application has not opened that IPv6 endpoint. A timeout instead means no useful response arrived within the limit; it is different from an immediate refusal. Do not fix either by disabling IPv6. An ordinary dual-stack browser can retry over IPv4, so seeing a page there would not prove IPv6 success.
For a mistyped name, curl may report error 6, meaning name resolution failed. Compare the spelling, then repeat the first command. A typo in a saved path reports a local write error; use pwd and the shown v4/index.html path. These are different from HTTP 404, where a reachable server says a requested resource is absent.
Let the Web Service Listen on IPv6
In this step, you will keep the working IPv4 listener and add a separate IPv6 listener. Switch to Guide Server. It begins in /home/labex/project/ipv6-guide/config. cat reads the prepared endpoint table and short target configuration:
cat endpoints.tsv
cat guide.conf
The guide belongs on 10.77.0.10 and fd77:7::10, port 8080. The welcome desk uses port 8081; preserve it. server_name chooses this site's name, root locates its original pages and index selects the homepage. Braces group a server; each directive ends with a semicolon.
ss reads the kernel's sockets. -l selects listeners, -t TCP, -n numeric addresses/ports and -p owning processes:
ss -ltnp
Find Nginx on IPv4 10.77.0.10:8080; there is no IPv6 guide listener yet. The desk's IPv6 :8081 socket does not serve the guide's port.
You will replace the whole short file with a complete template. cat > guide.conf writes to this file, replacing its previous content. <<'NGINX' begins a here-document: the shell takes all following lines literally until the line containing only NGINX. Paste the entire block, including that final marker. First, cp saves a local backup; the second filename is the copy:
cp guide.conf guide.conf.before
cat > guide.conf <<'NGINX'
server {
    listen 10.77.0.10:8080;
    listen [fd77:7::10]:8080 ipv6only=on;
    server_name guide.riverlight.test;
    root /opt/labex/ipv6-guide/www;
    index index.html;
    error_page 404 /404.html;
}
NGINX
listen opens an application endpoint. The new bracketed address is IPv6; ipv6only=on keeps that listener IPv6-only. The retained IPv4 line serves IPv4 independently. Address configuration alone could never create this listening socket.
The prepared guide-control command checks or loads only this course's independent service. web-check runs Nginx's configuration test without loading changes:
guide-control web-check
Expect syntax is ok and test is successful. If a semicolon, brace or address was mistyped, the error names the file and line. Nothing has been loaded. Repeat the complete template above, then check again. To return to the original working IPv4 configuration, cp guide.conf.before guide.conf restores your backup; check that file before loading. Do not restart platform Nginx or networking.
web-load tests again, then requests a reload. Reload preserves the course master process while it applies the saved configuration; a saved file by itself does not change the service:
guide-control web-load
ss -ltnp
Expect both 10.77.0.10:8080 and [fd77:7::10]:8080 owned by Nginx. If the log reports an occupied endpoint, compare this file with the full template and inspect ss; do not stop an unrelated service.
Switch to Guide Client. -w prints connection facts after the body. The quoted format contains \n for a newline; curl replaces %{remote_ip} with the actual peer address and %{http_code} with the response status:
curl --noproxy '*' -6 -fsS --max-time 3 -w '\npeer=%{remote_ip} status=%{http_code}\n' 'http://[fd77:7::10]:8080/'
Expect the Riverlight HTML, then peer=fd77:7::10 status=200. Read the content as well as the status: an unrelated default page with 200 would be wrong. This successful direct request isolates the application layer; you have not repaired the guide's name yet.
Point the Name at the Working IPv6 Service
In this step, you will correct only the target AAAA record and allow a real cache to update naturally. Begin in Guide Client. DNS, the Domain Name System, maps names to data. An A record supplies IPv4; AAAA supplies IPv6. The DNS query itself can travel over IPv4 and still return an IPv6 address.
dig queries DNS. @10.77.0.2 selects the prepared authoritative server, which owns this zone. +noall +answer hides other sections and shows answer rows:
dig @10.77.0.2 guide.riverlight.test A +noall +answer
dig @10.77.0.2 guide.riverlight.test AAAA +noall +answer
The A record is correct at 10.77.0.10. The AAAA currently says fd77:7::99, which does not match the working service. Now query the client's independent caching resolver at loopback 127.0.0.1:
dig @127.0.0.1 guide.riverlight.test AAAA +noall +answer
A row contains name, TTL, IN, record type and value. TTL means Time To Live: the remaining seconds for which a cached answer can be reused. The prepared zone uses 30 seconds. This query may cache the old address, which is normal.
Switch to Guide Server and read the complete zone:
cat guide.zone
$TTL 30 sets the default lifetime. @ means this zone's root. The SOA (Start of Authority) record includes the zone version, or serial, as its first number in parentheses. NS identifies the zone's authority. Names ending in a dot are complete names; short names such as guide are relative to riverlight.test. Preserve all records except the guide AAAA, and increment the serial from 1 to 2 for this revision. The serial records a zone version; it does not flush existing client caches.
Back up the file, then use the already taught here-document pattern to replace the full short zone. The single quotes around ZONE also protect $TTL from shell variable expansion:
cp guide.zone guide.zone.before
cat > guide.zone <<'ZONE'
$TTL 30
@ IN SOA ns.riverlight.test. admin.riverlight.test. (2 60 30 3600 30)
@ IN NS ns.riverlight.test.
ns IN A 10.77.0.2
guide IN A 10.77.0.10
guide IN AAAA fd77:7::10
desk IN A 10.77.0.10
desk IN AAAA fd77:7::10
contact IN TXT "Welcome desk opens at 10:00"
ZONE
dns-check runs the native BIND zone validator. It does not change live DNS:
guide-control dns-check
Expect loaded serial 2 and OK; here loaded describes the validator reading the file, not the running authority changing. If parsing fails, read the line number, repeat the full template and check again. cp guide.zone.before guide.zone restores the original file if needed; it also restores the old wrong AAAA, so it is a recovery starting point rather than the finished answer.
dns-load checks, then uses a private control channel to reload only this course's zone:
guide-control dns-load
Switch to Guide Client. Query authority and cache separately:
dig @10.77.0.2 guide.riverlight.test AAAA +noall +answer
dig @127.0.0.1 guide.riverlight.test AAAA +noall +answer
The authority should now return fd77:7::10. The cache can still show the old address until its remaining TTL expires. sleep 31 waits 31 seconds without changing any cache:
sleep 31
dig @127.0.0.1 guide.riverlight.test AAAA +noall +answer
Now expect the correct IPv6 address. No global cache flush or resolver edit is needed. If authority is still wrong, return to the saved zone and dns-load; if authority is correct but the cache still differs, read TTL and repeat the bounded wait. Deleting AAAA would remove IPv6 name access rather than repair it.
Finally, force a named IPv6 request:
curl --noproxy '*' -6 -fsS --max-time 3 -w '\npeer=%{remote_ip} status=%{http_code}\n' http://guide.riverlight.test:8080/
Expect Riverlight HTML and peer=fd77:7::10 status=200. A direct IPv6 success followed by a named failure points you toward DNS rather than rebuilding the listener.
Read and Download the Complete Guide Both Ways
In this step, you will use the complete guide through both address families and retain the protected desk and records. Begin in Guide Client. A correct homepage alone does not prove its detail link, styling or full download works.
Save all four original resources by the real guide name over IPv4. The prepared v4 folder holds only your downloaded bytes; each -o path names that resource's saved file:
curl --noproxy '*' -4 -fsS http://guide.riverlight.test:8080/index.html -o v4/index.html
curl --noproxy '*' -4 -fsS http://guide.riverlight.test:8080/visit.html -o v4/visit.html
curl --noproxy '*' -4 -fsS http://guide.riverlight.test:8080/style.css -o v4/style.css
curl --noproxy '*' -4 -fsS http://guide.riverlight.test:8080/programme.txt -o v4/programme.txt
Repeat through IPv6, saving separately so success cannot overwrite the IPv4 evidence:
curl --noproxy '*' -6 -fsS http://guide.riverlight.test:8080/index.html -o v6/index.html
curl --noproxy '*' -6 -fsS http://guide.riverlight.test:8080/visit.html -o v6/visit.html
curl --noproxy '*' -6 -fsS http://guide.riverlight.test:8080/style.css -o v6/style.css
curl --noproxy '*' -6 -fsS http://guide.riverlight.test:8080/programme.txt -o v6/programme.txt
cmp compares two files byte for byte. No output and a return to the prompt means equality; a reported difference means the resources disagree. Compare every resource, then read the complete programme:
cmp v4/index.html v6/index.html
cmp v4/visit.html v6/visit.html
cmp v4/style.css v6/style.css
cmp v4/programme.txt v6/programme.txt
cat v6/programme.txt
Read through WET WEATHER and the final synthetic-event note. A file's existence or size would not prove that this complete schedule and access information arrived correctly. If two wrong files match, cmp alone also cannot establish original content; the checks compare with the prepared originals and actual service.
Switch to Saved Guide. Select Open IPv4 saved guide, read the programme cards, then select Make a day of it to read the arrival/access information. Select Save the programme on that page to download the programme. Use the browser's Back button to return from the detail page to the homepage, then Back again to the viewer's selection page. Select Open IPv6 saved guide and repeat the same links and download. Both should be the same complete Riverlight guide.
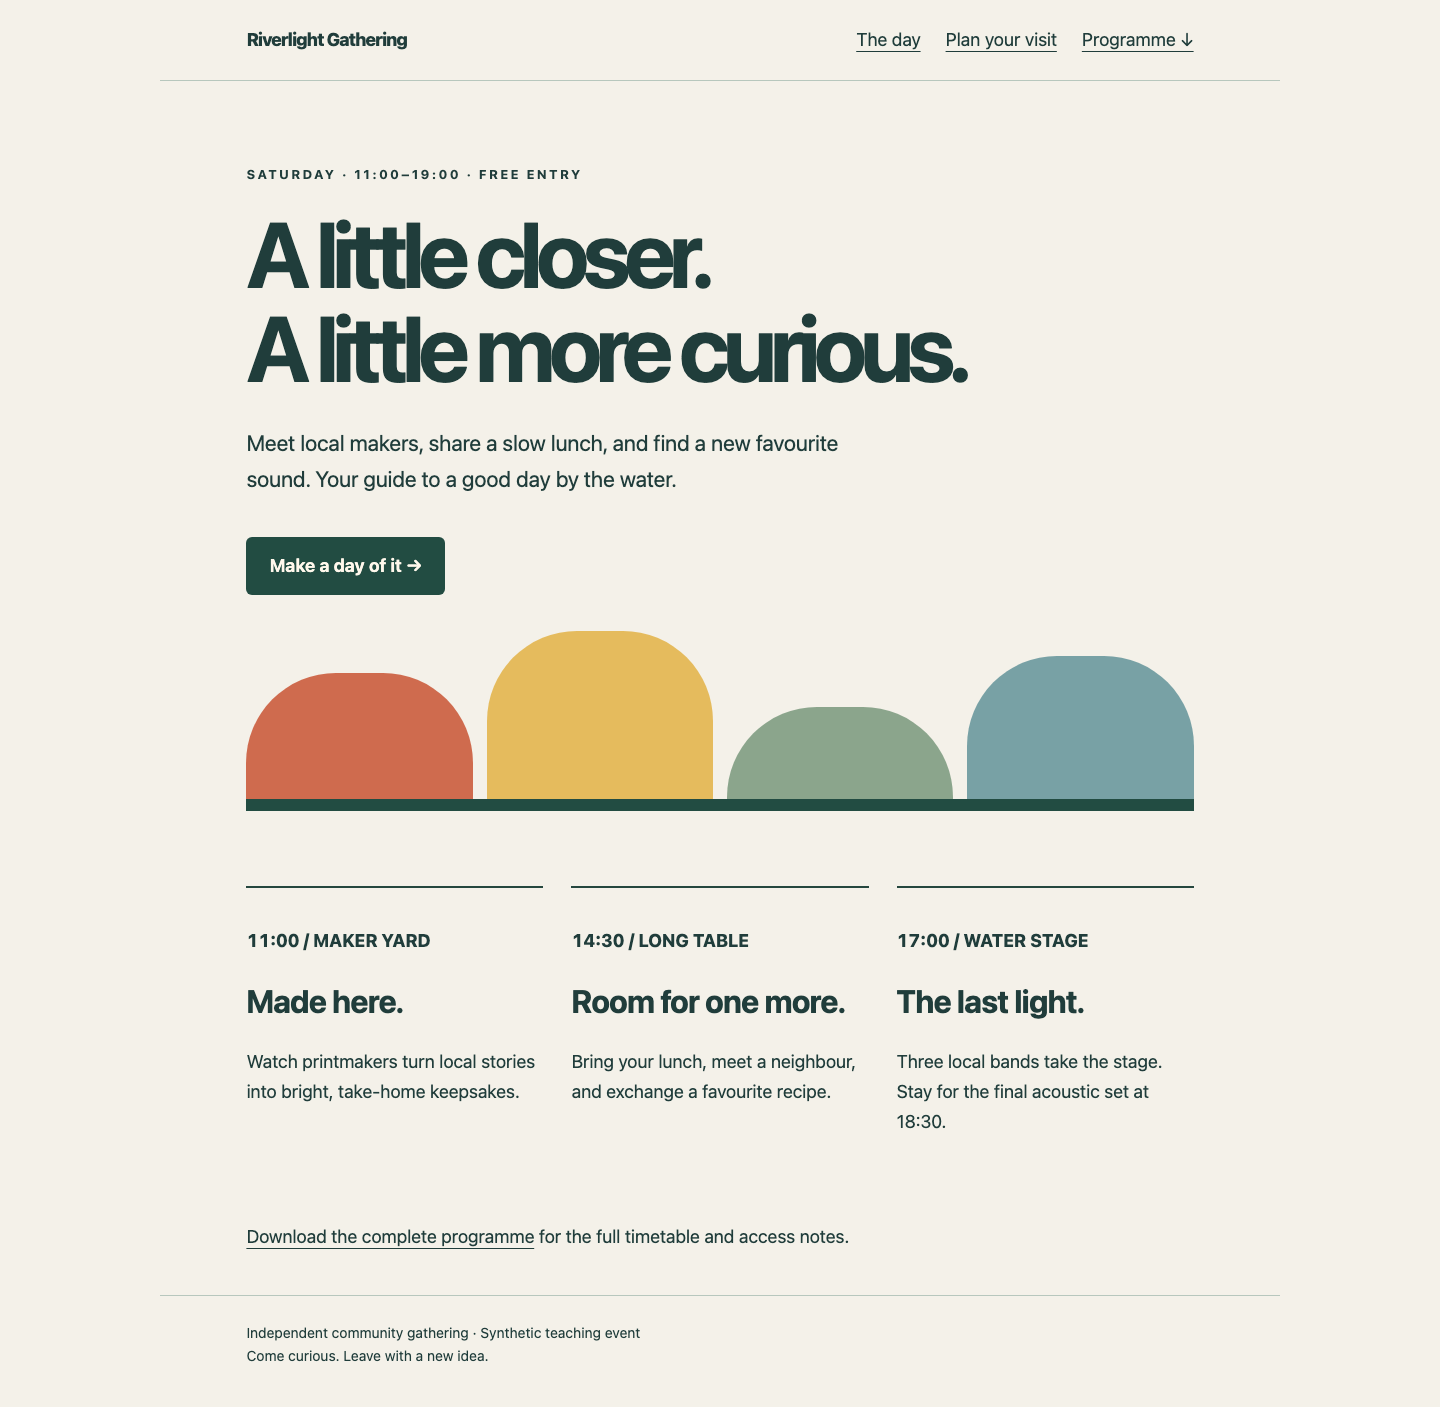
Read the three programme cards and use the visit and download links; this page is your actual saved guide.
This viewer reads only v4 and v6 files from Guide Client. It never fetches a missing file. If styling or a page is missing, return to Guide Client, repeat that exact family/resource save, then reload the browser page. The browser-to-viewer connection is a presentation path; your terminal's forced-family requests and actual peer establish IPv6, not the viewer's URL.
Switch to Guide Client. Keep the independent welcome desk available through both families:
curl --noproxy '*' -4 -fsS http://desk.riverlight.test:8081/
curl --noproxy '*' -6 -fsS http://desk.riverlight.test:8081/
Both return Welcome desk: open 10:00–20:00. Keep this site available. Check the retained A and TXT records:
dig @10.77.0.2 guide.riverlight.test A +short
dig @10.77.0.2 contact.riverlight.test TXT +short
Expect 10.77.0.10 and "Welcome desk opens at 10:00". If a protected value differs, restore it from the full original template while retaining the corrected guide AAAA, validate and reload. Do not copy source pages, add a proxy, replace a service process or change addresses to make a check turn green. The checks observe current services and saved results; ordinary GET and DNS queries may append native logs but do not load or repair your work.
Summary
You extended a working IPv4 guide with a real IPv6 listener, corrected its AAAA record and let a separate DNS cache update naturally. Forced-family requests delivered the same original homepage, arrival page, stylesheet and complete programme. You preserved IPv4, the welcome desk, other records and the prepared network. Reachability, name resolution, listening and correct application content are separate facts.


