

Docker vs Virtual Machines: Choose the Right Beginner Lab
Choose Docker or a virtual machine by the task you want to practice, with a real kernel experiment and clear boundaries for services, networking, storage, and isolation.
You want to practice Linux. One tutorial says to install a virtual machine; another starts with docker run ubuntu. Both give you a shell, but they do not give you the same system to administer.
Choose a container when the task is about running and packaging an application. Choose a full virtual machine when the task depends on a complete operating system: its boot process, kernel, disks, or system services. You can also run Docker inside a VM. That combination is useful when you want both a disposable Linux host and containers to inspect.
The decision starts with what you want to change and observe. Opening a Bash prompt is not enough to establish that an environment supports the next exercise.
Choose by the experiment, not the interface
| What you want to practice | A useful starting environment | What to verify first |
|---|---|---|
| Run an HTTP application and inspect its logs | Docker container | The image’s startup command, application port, and host mapping |
| Build an image containing your application | Docker-enabled host or VM | Docker daemon access and a working build context |
| Work with files, pipes, and ordinary shell commands | Either | Available utilities, shell, user identity, and file permissions |
| Enable a service and test it after a system reboot | Full Linux VM | The guest’s init system and whether rebooting is permitted |
| Learn OS installation, partitions, or boot recovery | Full VM with suitable virtual disks | Disk ownership, console access, and a recoverable starting state |
| Compare applications using different dependencies | Separate containers | Compatible images and the network/data boundaries between them |
| Test a different Linux kernel | A VM booting that kernel | Guest architecture and virtualization support |
This comparison assumes ordinary Linux containers and a VM that you can administer. Specialized containers can run init systems, and managed VMs can restrict administration. Neither label guarantees every capability in the table.
If you are choosing among WSL, a local VM, and online practice environments, the Linux learning roadmap provides a broader starting sequence. Here, the narrower question is which operating-system boundary your Docker or Linux exercise needs.
A different distribution does not necessarily mean a different kernel
An operating system includes both a kernel and user-space programs. The kernel manages resources and provides system calls. User space includes tools such as the shell, package manager, and libraries.
In the ordinary Linux container model, containers use the kernel of the system running the container runtime. A VM instead boots a guest operating system with its own kernel. Docker’s container introduction explains this distinction and describes using containers and VMs together.
You can observe the difference without installing a second operating system. On a Linux Docker host, run:
uname -r
. /etc/os-release
echo "$PRETTY_NAME"
Then inspect the kernel and distribution information inside an Alpine container:
docker run --rm alpine:3.23 sh -c 'uname -r; . /etc/os-release; echo "$PRETTY_NAME"'We ran these commands in a LabEx Ubuntu 22.04 instance VM with Docker Engine 20.10.21 on September 7, 2026. The host reported Ubuntu 22.04.2 LTS, while the container reported Alpine Linux v3.23. Both reported the kernel release 5.15.0-56-generic.
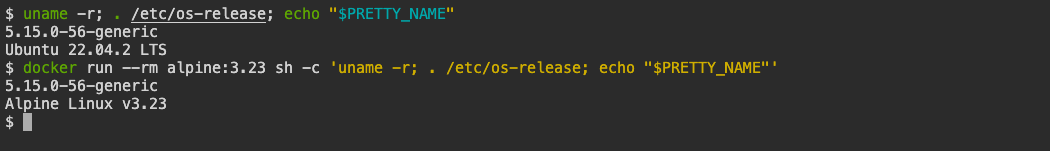
Two user spaces, one running kernel in this experiment. The screenshot is a boundary check, not a performance benchmark.
The /etc/os-release file describes the user-space distribution whose filesystem you are reading. uname -r reports the running kernel release. Taken together with the documented container architecture, these observations explain why an Alpine container on this host is not a separately booted Alpine VM.
Your output will differ with the host and image version. The alpine:3.23 tag can also receive updates. Matching release strings alone would not prove shared kernels in every possible environment; two independent VMs can boot the same kernel version. The interpretation here depends on knowing that the second command starts an ordinary container on the inspected Docker daemon.
Docker Desktop adds a layer worth naming
“Docker versus a VM” can be a misleading choice on a laptop. Docker Desktop runs Linux containers through a Linux VM on macOS and Windows. Docker Desktop for Linux also uses a VM, as its Linux installation documentation explains.
Consequently, the kernel you observe inside a Linux container on Docker Desktop belongs to that Linux environment. It is not the macOS kernel, and it is not evidence that Docker installed a complete guest OS for every individual container.
For troubleshooting, draw the actual stack you use:
Linux server example:
physical or virtual Linux host → Docker Engine → application containers

Docker Desktop example:
laptop operating system → Docker Desktop's Linux VM → application containers
This matters when instructions refer to “the host.” They may mean the machine running the Docker daemon rather than the terminal where you typed the command. A remote Docker connection introduces the same distinction.
Before following a lab, establish three facts: where the Docker daemon runs, where your application runs, and where the client request originates. Those locations affect file paths and network access far more directly than the appearance of your terminal window.
A shell is not the same as a booted server
Suppose your goal is to start a service, enable it at boot, reboot the machine, and verify that it returns. A minimal application container is usually the wrong starting environment for that exercise.
The container’s primary process might be a shell, Python, or a web server. It may not include a service manager or the surrounding boot environment expected by a system-administration tutorial. Installing a missing command does not automatically reproduce those system conditions.
By contrast, a full VM lets you work with the guest’s booted operating system, subject to the permissions of the VM provider. That is a better match for exercises involving startup configuration and recovery. You must still check that the environment allows the required reboot, console access, or disk operations.
For a container exercise, ask a different question: what command starts the application, what keeps it running, and what evidence is available if it exits? Docker’s run reference describes the foreground and detached execution model. Treating a container as a small, permanently running server often hides the very lifecycle behavior you are trying to learn.
Storage and networking need explicit boundaries in both cases
With a VM, files on its virtual disk can survive an ordinary guest reboot. Deleting that disk is a different operation. With a container, files in its writable layer survive stopping and starting that same container, but they are lost when that container is removed. Persistent mounts give container data a separate lifecycle. Docker’s storage overview documents those storage locations.
The useful comparison is therefore not “VMs save files and containers do not.” Ask which resource contains the files and which action removes that resource. A VM snapshot and a Docker image are also different artifacts; an image is not a complete backup of a running host or all mounted data.
Networking has a similar trap. Seeing a web server listening inside either environment does not establish a working browser path from your laptop. VM networking may involve NAT or a bridged interface. An ordinary Docker bridge example uses published ports for a host-side entrance. An online lab can add a separate preview gateway.
Use a small HTTP request to check one boundary at a time. The EXPOSE versus publish experiment shows how an application can answer inside a container while remaining unreachable through the host URL. That diagnosis is more useful than switching environment types whenever a browser connection fails.
Isolation is a configuration question, too
A VM has a separate guest kernel; an ordinary Linux container shares its runtime host’s kernel. That is a meaningful architectural difference. It is not a complete security verdict about either environment.
Host directory sharing, device access, daemon permissions, network exposure, and the code you run all affect the boundary. Giving an environment broad access to your personal files can undermine the separation you expected. Docker’s Engine security documentation discusses namespaces, capabilities, daemon access, and configuration risks.
For beginner practice, use disposable environments and files created for the exercise. Do not add privileged mode or mount the host’s root filesystem merely to make an incompatible tutorial proceed. If the lesson requires full system administration, choosing a suitable VM usually makes the intended boundary easier to understand than continually expanding a container’s privileges.
Compare the work you will maintain
A local VM asks you to maintain a guest OS, its disk, updates, and recovery method. Containers ask you to maintain images, runtime configuration, mounts, and the Docker host underneath them. A browser lab moves some environment setup to the provider, but you must still understand its session and persistence rules.
There is no universal resource-cost result here. The number of applications, assigned VM memory, image layers, host architecture, and storage workload all change the comparison. This article did not benchmark startup time, memory consumption, or cloud pricing. Use the published requirements of the specific environment you intend to run rather than transferring a number from an unrelated setup.
For your first lab, write one sentence describing success:
- “I can rebuild an application image and start a new container from it” points toward Docker practice.
- “I can repair a service and verify it after a guest reboot” points toward a full Linux VM.
- “I can explain both the host and its containers” points toward Docker inside a VM.
The LabEx Docker course provides Docker-enabled Ubuntu environments for container practice. The Linux path is the broader entry for operating-system skills. Choose the activity whose environment supports your success condition, then record what state must survive when you stop, restart, or recreate it.
References
- Docker: What is a container? — container and VM architecture.
- Docker Desktop on Linux — the VM used by Docker Desktop.
- Docker: Running containers — application execution and lifecycle.
- Docker storage overview — writable layers and external storage.
- Docker Engine security — configuration and isolation boundaries.
- LabEx Docker for Beginners — course scope and supplied environments.