A login record tells you someone signed in to a machine. Another record tells you a command was approved. Can you connect the two? Event correlation means comparing records to see whether they describe related activity.
Security Logs · Lesson 5
Event Correlation
Learn how to connect security records using time, host, account, and session information.
Reading Two Records
SSH lets you sign in to another machine. After signing in, a user can request permission to run a command as another account using sudo. Below are two simulated records from the same date, written with matching field names for practice. Real logs can use different names or leave some fields out.
t=09:14:02Z      source=ssh   host=web-01 account=alex session=42 login=accepted
t=11:15:10+02:00 source=sudo  host=web-01 account=alex session=42 decision=allowed
The source field names the tool reporting an event. The host field names the machine where it occurred. Both records report activity under the account alex. Identifying the person who used that account would take more evidence.
A teammate says that Alex personally made the sudo request. What do the records establish so far?
Comparing Event Times
The t field contains the recorded time. In the first record, Z marks UTC, a common reference for comparing clocks. The second record uses +02:00, two hours ahead of UTC. Subtract two hours from 11:15:10 to get 09:15:10 in UTC.
Now compare 09:14:02 and 09:15:10. The login was recorded first. Events close in time may still come from separate logins.
On another day, a login is recorded at 09:14Z and a request at 11:13+02:00. What is the order?
Checking the Host and Session
A session is the period of activity from signing in to signing out or disconnecting. In these practice records, the SSH entry includes the session ID linked to the accepted login. The two sources use the same session ID for that login on the same host. The first two records show host=web-01 and session=42, which links the sign-in and the request to one session.
A session number is local to its host in these samples. The following record has the same account and session number and appears just seconds later.
t=09:15:18Z source=sudo host=web-02 account=alex session=42 decision=allowed
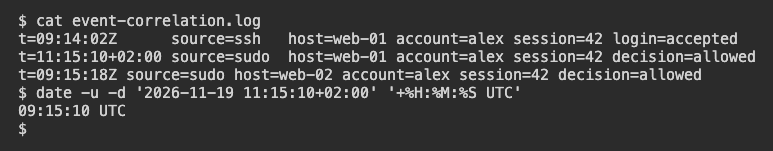
The terminal displays the three simulated records and uses Ubuntu’s date command to confirm the UTC conversion.
How does the third record relate to the original SSH session?
Stating What the Records Support
On web-01, the login was accepted and sudo gave permission to run a command during that session. That is where the available evidence ends. To learn how the command finished, look for a record that reports its result. A session can contain several commands, so match the result to the specific request. Keep the outcome unknown if you cannot find a matching record.
Which new record could resolve whether that command finished successfully?
To practice filtering and comparing another set of authentication and sudo records, try System Log Analysis.
Lesson complete
You finished Event Correlation
You can now use more than one security record to make a claim and identify what still needs checking.
Identify the account recorded for an event.
Convert timestamps to a common time zone before comparing them.
Use the host and session together to link activity.
State what the records establish and look for evidence that answers the remaining question.
Keep your learning progress
Create a free account to save this lesson and continue learning on any device.
Create a free account